Cloud & DevOps / Infrastructure blueprint
Silsila Hardened Pipeline
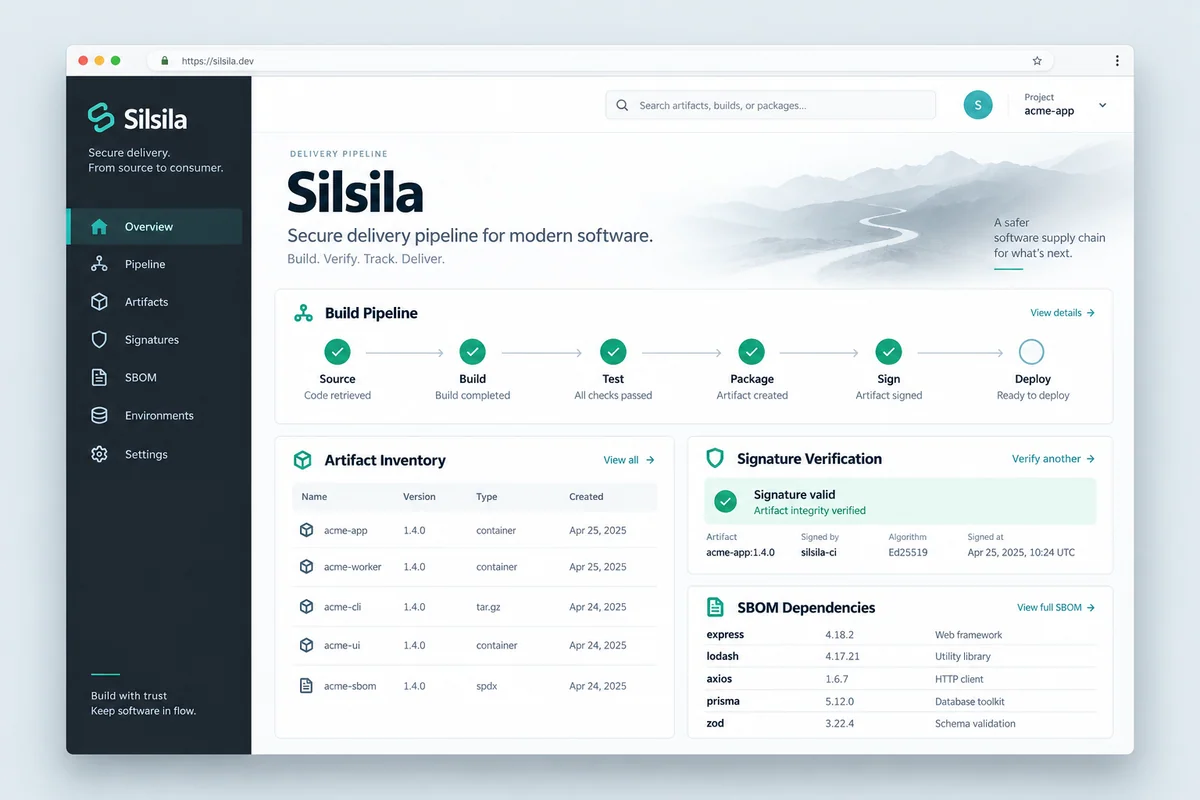
A secure software delivery blueprint connecting image scanning, SBOM generation, artifact signing, and Kubernetes admission policies.
- Focus
- Infrastructure & platform engineering
- Project type
- Infrastructure blueprint
- Core technologies
- Terraform · EKS · Cosign · Kyverno
Context
The engineering problem
Scanning source code is only one part of supply-chain security. Teams also need to trace built artifacts, verify what enters a cluster, and observe workloads after deployment.
Architecture at a glance
A simplified map of the intended relationships in this blueprint. Integration gaps are described in the implementation scope; arrows do not establish a running deployment.
- clientGitHub sourceRunner workflowserviceBuild & scan
- serviceBuild & scanSource inventoryserviceSBOM & signing
- serviceSBOM & signingIntended provenance bindinginfraECR registry
- infraECR registryVerification policygatewayKyverno / EKS
- gatewayKyverno / EKSWorkload observationinfraFalco runtime
All system components (6)
- GitHub sourceclient
- Build & scanservice
- SBOM & signingservice
- ECR registryinfra
- Kyverno / EKSgateway
- Falco runtimeinfra
Approach
Implementation decisions
Trace the artifact
Syft inventories source dependencies and Cosign signs the resulting SBOM. Binding that inventory to the final container image is a separate integration step.
Check at admission
A Kyverno policy describes signature checks for the configured registry. Its signing-key placeholder and namespace exceptions must be resolved and tested in the target cluster.
Observe runtime behavior
Falco rules and observability modules provide a separate layer for detecting activity after admission.
Explore the implementation
Start with the source.
These entry points connect the architecture to the implementation.
- Infrastructure composition ↗terraform/main.tf
- Signature verification policy ↗kubernetes/kyverno/cluster-policies/verify-image-signatures.yaml
- SBOM generation ↗scripts/generate-sbom.sh
- Signing infrastructure ↗terraform/modules/signing_infrastructure/main.tf
Implementation scope
Terraform modules, Kubernetes policies, and automation scripts form a reference software factory. The SBOM script inventories the source directory; image provenance and the admission policy's key placeholder need integration before deployment.